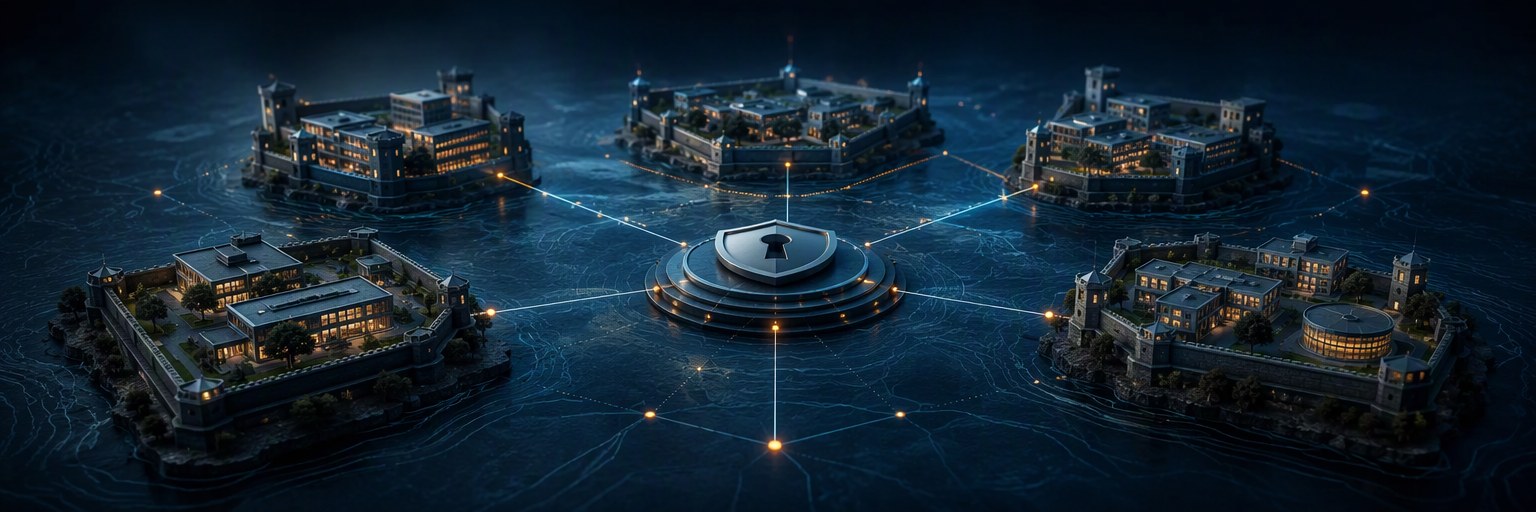
A Distributed Autonomous Organization is an architectural approach for giving connected groups the ability to manage their own people, information, and workflows within a shared platform. Each participating organization can operate within defined boundaries while benefiting from common infrastructure, reusable functionality, and coordinated services.
The concept can be adapted to professional networks, government agencies, membership organizations, research collaborations, and other environments where local independence must coexist with shared objectives. Its implementation depends on the client’s governance model, operational requirements, and desired degree of autonomy.
Shared Foundations, Local Control
A DAO architecture allows an organization to distribute responsibility without requiring every participating group to maintain a separate technical platform.
Each group could manage its membership, assign roles, maintain content, and administer its own processes. Shared services could provide identity management, search, reporting, communications, and integrations across the wider network.
The boundaries are configurable. Some implementations may require substantial separation; others may encourage collaboration and shared information. The architecture can support both through explicit rules governing ownership, visibility, and authority.
A Spectrum of Autonomy
Autonomy can apply to different parts of an organization. A group might control its publishing while following centrally defined policies, or manage its membership and workflows while sharing selected information with other participants.
Potential configurations include:
- Administrative autonomy: Local administrators manage users, permissions, and organizational settings.
- Content autonomy: Groups create, review, and publish information within their own spaces.
- Operational autonomy: Participants maintain workflows suited to their responsibilities.
- Governance autonomy: Groups make decisions through defined approval, representation, or voting processes.
- Information autonomy: Organizations determine which records remain restricted and which become available across the network.
- Technical autonomy: Where required, components operate in separate environments connected through agreed interfaces.
These capabilities can be combined according to the project. A centrally coordinated network, a federation of independent organizations, and a collaborative membership community may each require a different balance.
Governance That Reflects the Organization
The governance model establishes who can make decisions, which rules apply, and how disagreements or exceptions are handled. Technology then supports those arrangements through permissions, workflows, and recorded actions.
An implementation could provide delegated authority, elected representatives, proposal review, member voting, or approval thresholds. Different decisions may follow different processes, with some responsibilities remaining explicitly assigned to accountable individuals.
Automation can carry out defined rules, issue notifications, and coordinate routine tasks. Human judgment remains available wherever the organization requires review, discretion, or intervention.
This model can be implemented using conventional application architecture. Blockchain, tokens, and smart contracts are optional design choices where they serve a specific requirement.
Information Boundaries and Shared Visibility
A distributed organization needs clear rules for how information moves between groups. Private working material, shared resources, and public results may each require different treatment.
A platform could allow participants to collaborate behind controlled access boundaries and publish selected outcomes to a common website. Alternatively, organizations could retain separate public identities while contributing approved information to a network-wide directory or reporting service.
Search and reporting would follow those same permissions. Shared infrastructure should preserve each participant’s intended control over its information.
Potential Applications
The DAO approach can support a broad range of organizational structures:
- Professional associations: Chapters manage local membership and activities while sharing national resources.
- Government networks: Departments or jurisdictions administer their own workflows within a coordinated service.
- Research collaborations: Teams maintain controlled workspaces and share approved findings.
- Education and training: Participating organizations manage learners and programs using common learning resources.
- Nonprofit coalitions: Independent members coordinate initiatives while retaining their identities and responsibilities.
- Enterprise groups: Business units operate distinct processes within a shared technology foundation.
These examples represent possible configurations. Discovery would establish which capabilities provide value for the client’s particular organization.
Architecture and Integration
An implementation could use Drupal groups, structured content, role-based permissions, workflow tools, and APIs as part of its foundation. Requirements may also call for multidomain presentation, external identity providers, or connections to existing business systems.
Logical separation within one application and physical separation across infrastructure offer different benefits and responsibilities. The appropriate approach depends on security requirements, information ownership, scale, and operating resources.
The design should also account for organizational change. Groups may join, merge, separate, or leave, requiring defined processes for membership, records, access, and data export.
Bespoke Implementation
I approach a DAO project by defining the participating organizations, their responsibilities, and the capabilities they need to control. From there, I establish the shared services, governance rules, information boundaries, and integrations that connect them.
The resulting platform can begin with a focused set of organizational spaces and develop into a broader network as requirements mature. The objective is a shared technical foundation that supports meaningful independence and purposeful collaboration.